Protection of Sensitive Data
Ensuring that financial data remains secure and inaccessible to unauthorized entities.
Portfolio
Strengthening Security for Fintech App Bloon with AWS CloudFront
Fintech
Industry
5 Experts
Team size
240 Days
Timeline
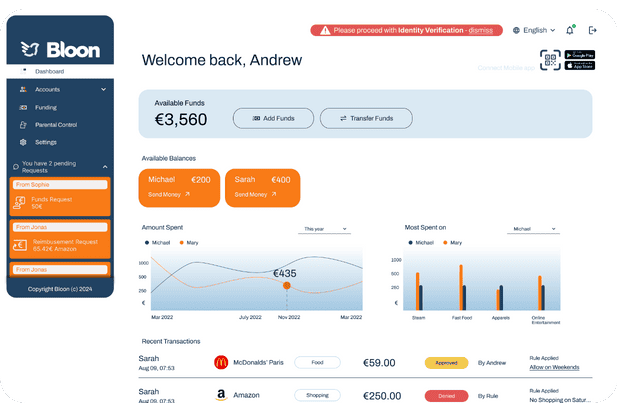
Bloon, a prominent fintech application, recognized the critical need to fortify its security measures to safeguard sensitive financial data and ensure uninterrupted service delivery. With AWS CloudFront, Bloon aimed to leverage advanced security features to mitigate potential threats and enhance its security posture and ensure uninterrupted service delivery.
Ensuring that financial data remains secure and inaccessible to unauthorized entities.
Implementing measures to mitigate common threats like DDoS attacks, SQL injection, and cross-site scripting (XSS).
Adhering to industry regulations such as PCI DSS to maintain trust and credibility among users.
Establishing a system for real-time monitoring and logging to promptly detect and respond to security incidents.
Our solution
Bloon implemented a comprehensive security strategy using AWS CloudFront:
1.1 Origin Access Identity (OAI) for S3
Bloon configured an Origin Access Identity (OAI) and associated it with the CloudFront distribution to restrict direct access to the S3 bucket containing static content.
A bucket policy was implemented to allow access only to requests originating from CloudFront, enforced through the OAI.
Security groups were configured for EC2 instances hosting dynamic content, permitting inbound traffic solely from CloudFront IP ranges and blocking direct access.
Network ACLs were utilized at the subnet level to impose additional security controls and restrict unauthorized access.
CloudFront was configured to include a custom header (X-Origin-Auth) with each request to the origin.
Bloon's application server validates the presence and value of the X-Origin-Auth header to ensure requests originate from CloudFront, enhancing origin validation.
2.1. AWS WAF Configuration
Bloon created a Web Application Firewall (WAF) ACL and associated it with CloudFront to filter incoming requests.
AWS Managed Rules were enabled to protect against common threats such as SQL injection and XSS, providing immediate security against known vulnerabilities.
Custom rules were established to implement rate limiting, restricting the number of requests from a single IP address to mitigate DDoS attacks.
Geo-blocking was employed to block requests from specific countries known for malicious activity, reducing the risk of potential attacks.
Bloon enabled logging for the Web ACL, directing logs to an S3 bucket for analysis and auditing.
CloudWatch alarms were configured using WAF metrics to alert administrators of anomalous activity, such as spikes in blocked requests, facilitating prompt response to potential threats.
Why OnGraph
The implementation of AWS CloudFront’s advanced security features yielded significant outcomes for Bloon:
Bloon enhanced data security by effectively protecting sensitive financial data from unauthorized access and potential breaches. It successfully mitigated common threats like DDoS attacks, SQL injection, and XSS, ensuring service integrity and availability.
10X
Protection against DDoS attacks. Mitigate DDoS attacks by distributing traffic across multiple edge locations.
50%
Reduction in latency. Faster load times and reduced latency enhanced user satisfaction.
60%
60% reduction in bandwidth costs. Efficient caching reduced the load on origin servers, leading to lower operational costs.
99.99%
Improved Uptime to 99.99%. With over 300 edge locations globally, it ensures low latency and high availability.
Ratings
Rated 4.5 for our work environment and learning opportunities.
5/5 stars for quality, reliability, ability and overall delivery.
3.9 stars — 94% recommend us and 92% approve of the CEO.
Recognition
Recognized for quality and credibility.
Awards and certifications earned by consistently delivering excellence.

Our experts are online · Free consultation
Our experts are available to discuss your requirements and to become your tech partner.